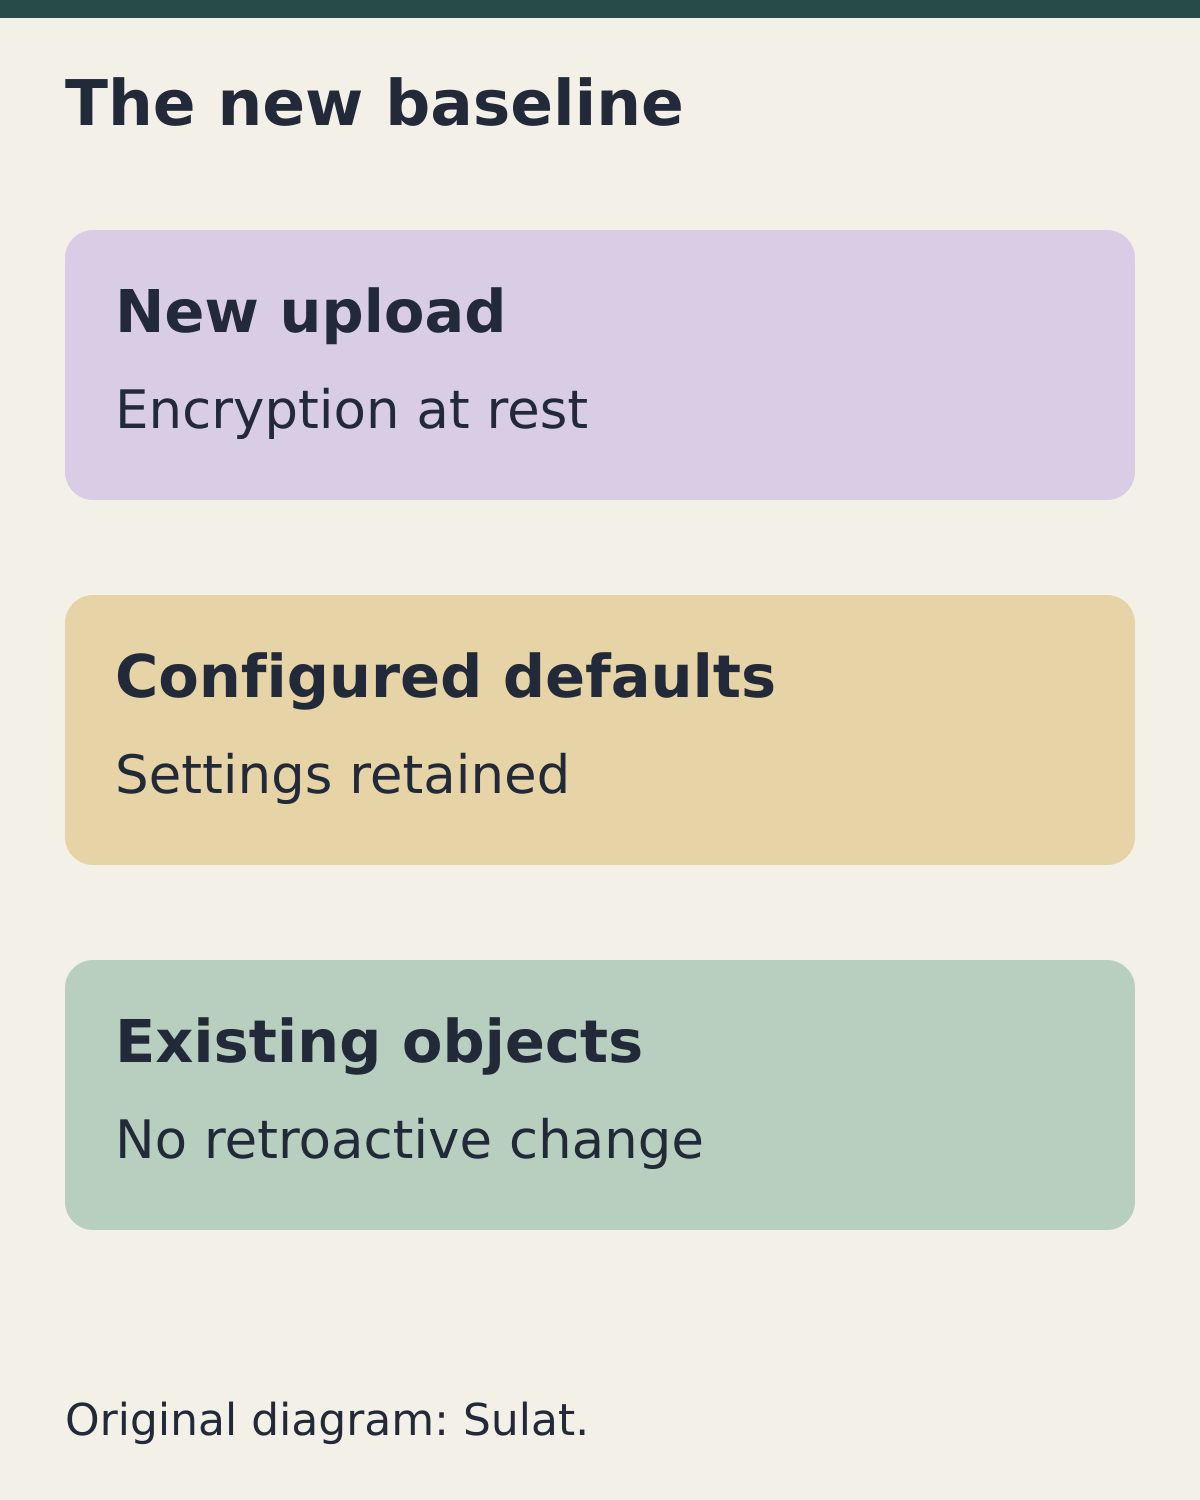
Amazon S3 now encrypts every new object upload by default. Announced on 5 January, the change applies across AWS Regions, including China and GovCloud. AWS says the baseline adds no charge or performance penalty.
Buckets without a configured default now use S3-managed server-side encryption. Existing encryption settings stay intact. Existing objects are not retroactively encrypted, and server-side protection at rest is not end-to-end encryption.
The change removes an opt-in step from storage security. CloudTrail data-event logs can show automatic encryption; console and other reporting updates are expected over the coming weeks. Data-event logging costs extra.
AWS identity belongs to its owner. No endorsement.
Discover more from Sulat AI & Tech News
Subscribe to get the latest posts sent to your email.