Node.js has published security updates for the 26.x, 24.x and 22.x release lines. The patched versions are v26.13.1, v24.22.3 and v22.23.5. The project says the highest severity issue fixed in this release is high, and that end-of-life versions are also affected. Operators are told to move to a supported, patched line.
The official announcement also lists dependency updates that address public vulnerabilities: llhttp on 22.x, 24.x and 26.x, undici on 24.x and 26.x, and sqlite on 22.x and 24.x.
🔐 Node.js security updates are now available!
November 11, 2026
Including the following dependency updates to address public vulnerabilities:
– llhttp on 22.x, 24.x, 26.x
– undici on 24.x, 26.x
– sqlite on 22.x, 24.x
Available for 26.x, 24.x, 22.x Node.js release lines
Security researcher Chris Rohlf, whom the Node.js project thanks in collaboration with Claude and Anthropic Research on several of the reports, says operators should patch their Node.js deployments this week. In a post quoting the official announcement, he wrote that Claude was able to discover, chain and remotely exploit three of the bugs: CVE-2026-123864, CVE-2026-123866 and CVE-2026-123874. He describes the first two as remote memory disclosures, and says the third can be leveraged for remote code execution, but only if the app uses stream.respondWithFile or respondWithFD.
The official advisory describes CVE-2026-123874 as a use-after-free that lets an unauthenticated client corrupt server memory when the application serves a file with those APIs, and it lists that issue on the 24.x and 26.x lines. It does not itself call the issue remote code execution.
You’ll want to patch your nodejs deployments this week. Claude was able to discover, chain and successfully remotely exploit CVE-2026-123864, CVE-2026-123866 (another bug collision), and CVE-2026-123874. The first two are remote memory disclosures and the third can be leveraged for RCE, but requires the app to use stream.respondWithFile/FD
November 11, 2026
The issues Rohlf highlighted
CVE-2026-123864, rated high, is an HTTPS flaw. The advisory says an unauthenticated client can read memory belonging to other connections, including TLS private keys and other users’ requests. Cleartext node:http is not affected. It hits 22.x, 24.x and 26.x. The project thanks Rohlf in collaboration with Claude and Anthropic Research for the report, and Matteo Collina, credited as mcollina, for the fix.
CVE-2026-123866, also high, is an HTTP/2 issue in which stream teardown can send freed response memory to a peer, including the contents of other connections’ response buffers. It affects 22.x, 24.x and 26.x. Official thanks go to aidan02 for reporting it and to Collina for the fix. Rohlf’s post includes this CVE among the three he says Claude found, and he calls it “another bug collision.”
CVE-2026-123874, rated high, is the HTTP/2 file-serving case above. The only precondition the advisory states is that the application serves a file with stream.respondWithFile() or stream.respondWithFD(). It is listed for 24.x and 26.x, with the same Rohlf, Claude and Anthropic Research credit, and Collina as the fixer.
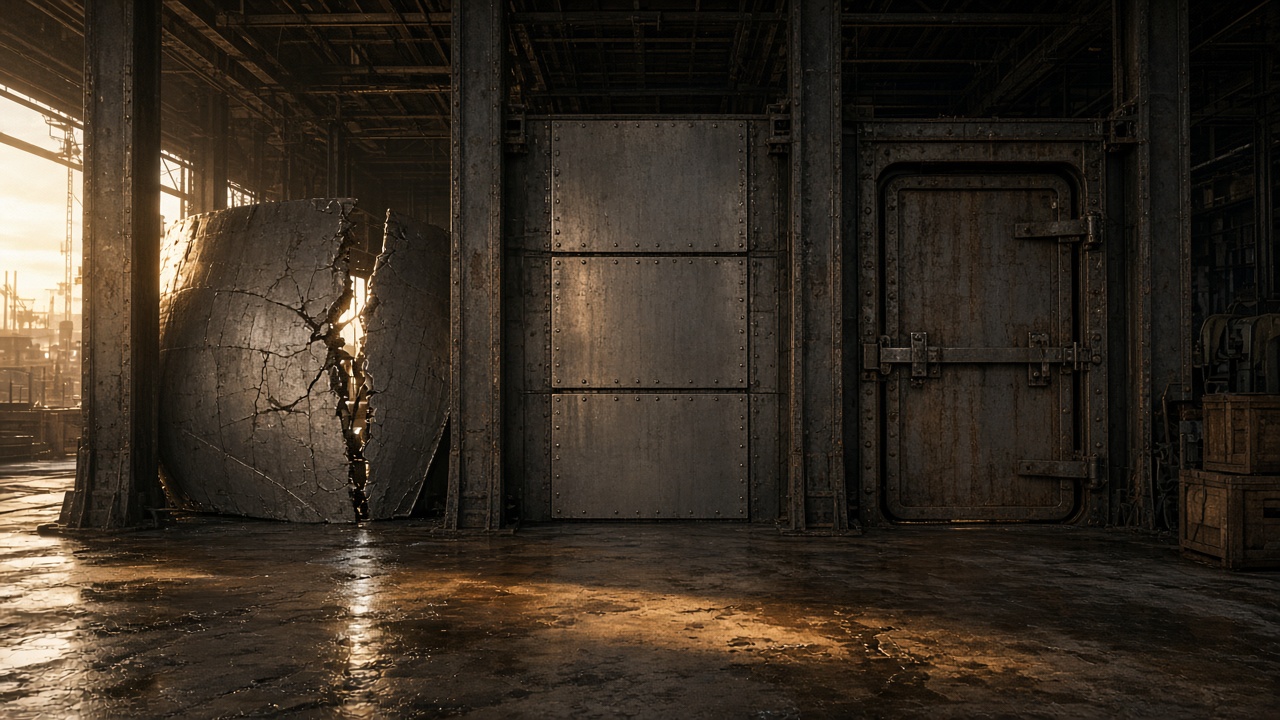
| Bay | What it shows |
|---|---|
| The open seam | An unpatched runtime still exposed to the bugs in this release |
| Three sealed plates | The patched builds: v22.23.5, v24.22.3 and v26.13.1 |
| The barred hatch | The high-severity HTTP/2 file-serving case, which the advisory says applies when an app uses stream.respondWithFile() or respondWithFD() |
A broader high-severity release
The advisory lists 16 issues in all: seven high, six medium and three low.
The other high issues, in the project’s short form, are:
| CVE | Official summary | Lines | Report credit |
|---|---|---|---|
| CVE-2026-123863 | An HTTP/2 remote abort that can terminate the process | 24.x, 26.x | Chris Rohlf in collaboration with Claude and Anthropic Research |
| CVE-2026-123865 | HTTP/2 sessions that never clean up if a protocol error hits during shutdown, leaking memory and file descriptors | 22.x, 24.x, 26.x | pimterry |
| CVE-2026-126051 | A remotely triggerable uncaught exception in TLS servers | 24.x, 26.x | pimterry |
| CVE-2026-123872 | TLS 1.2 renegotiation that can change the server name and bypass client certificate authentication | 22.x, 24.x, 26.x | pimterry |
Rohlf, Claude and Anthropic Research are also thanked on a medium-severity HTTP/2 crash when a respondWithFile() download is cancelled (CVE-2026-123875), listed for 22.x, 24.x and 26.x, and on a low-severity zlib assertion (CVE-2026-123862).
The medium-severity items include further HTTP/2 memory and crash bugs, TLS and certificate-handling issues, and a proxy-credential leak in an error message. The same advisory thanks other researchers for the remaining reports, including Trail of Bits (OpenAI) for a low-severity Permission Model disclosure in recursive fs.watch (CVE-2026-123829).
What operators should do
The project says the updates are available for all three supported lines, and that end-of-life versions are always affected when a security release occurs. The patched builds are v22.23.5, v24.22.3 and v26.13.1. The advisory points people to the Node.js release schedule and the project’s security policy.
Discover more from Sulat AI & Tech News
Subscribe to get the latest posts sent to your email.