Uber is notifying drivers that their personal data was exposed when an attacker used a vendor’s stolen credentials to reach Uber’s account with that vendor, according to Uber’s notice to the California attorney general. An Uber spokesperson named the vendor as Fireworks.ai, and TechCrunch reports the data includes driver’s licence details.
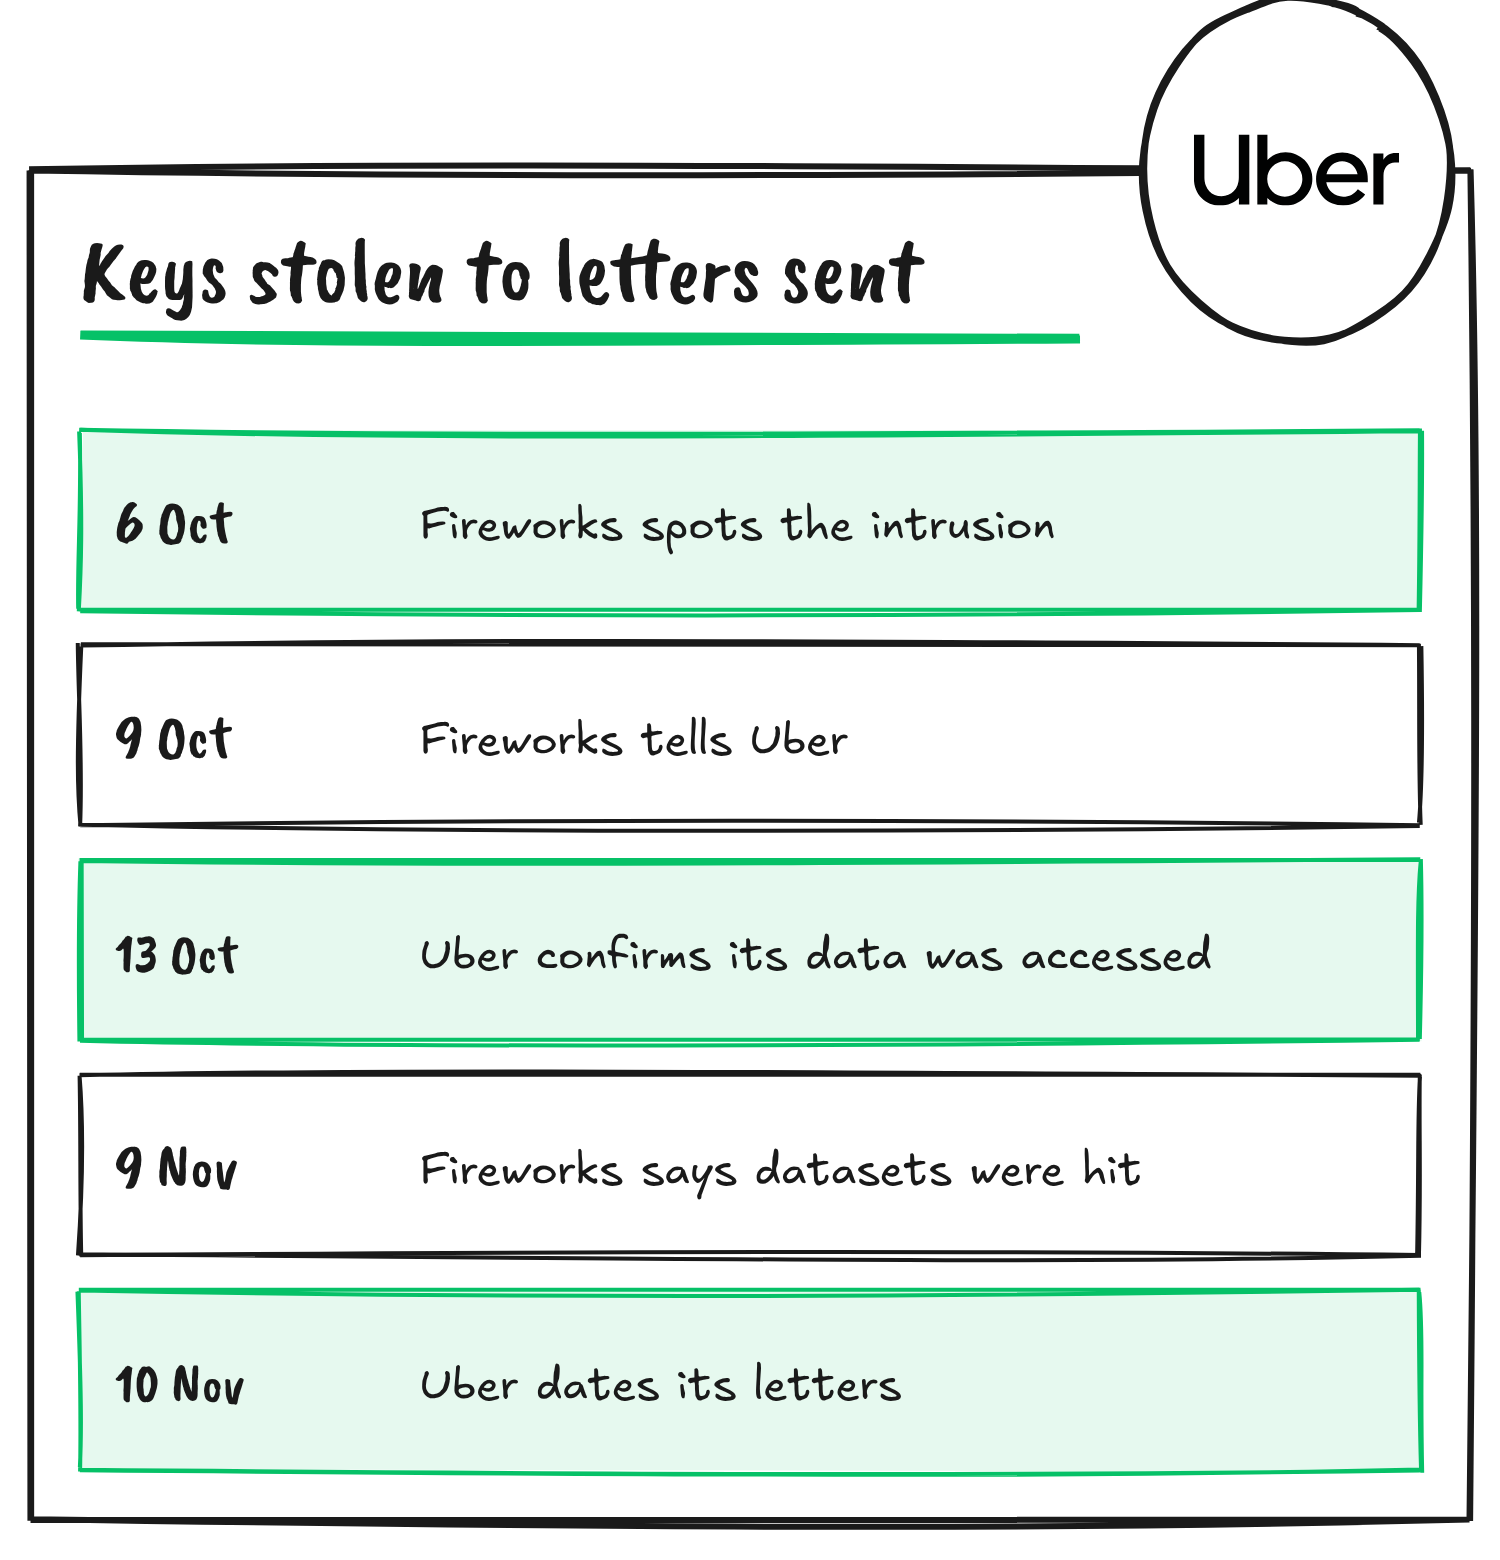
The Wall Street Journal reported the notifications on 13 November (US time). Uber’s letter, dated 10 November, doesn’t name the provider. The spokesperson did, telling the Journal and TechCrunch: “The notices to drivers are in relation to a security incident impacting one of our third-party vendors, Fireworks.ai, which had access to some Uber data.”
Uber is notifying users that their personal information was exposed in a breach involving one of the company’s service providers. https://t.co/HH76IcZw2H
— The Wall Street Journal (@WSJ) November 13, 2026
What Uber’s notice says
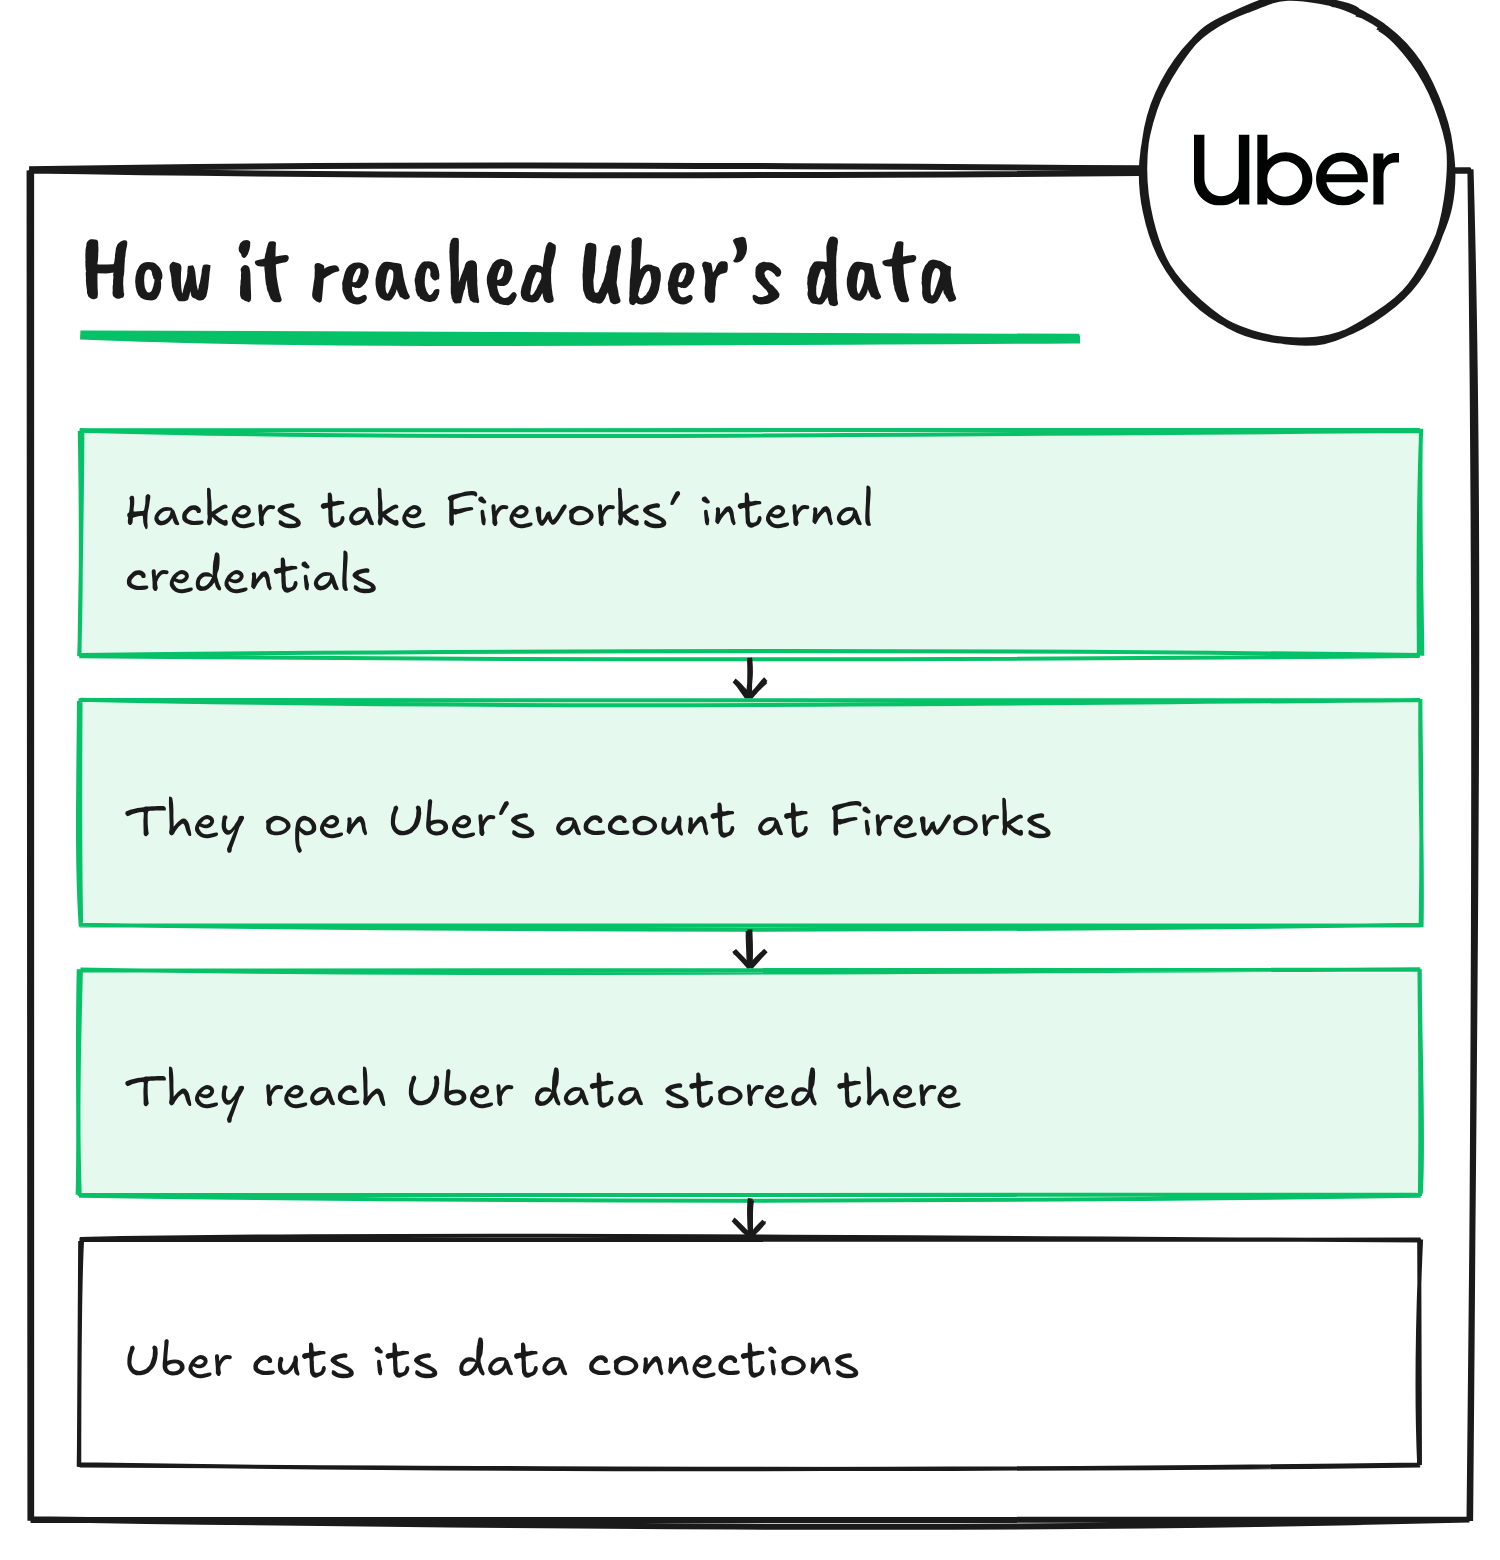
On 9 October, Uber says, a service provider told it that an unauthorised third party had compromised the provider’s internal credentials and used them to access Uber’s account with the provider. Uber says it cut its data connections with the provider straight away and opened an investigation. On 13 October, the investigation concluded that the attacker had used the credentials to access Uber data connected to the provider.
Uber is offering affected people credit monitoring and fraud assistance through Cyberscout, a TransUnion company. Enrolment has to happen within 90 days of the letter’s date. The notice says Uber hasn’t identified any misuse of the data to date. The California filing lists the breach date as 7 October.
How many people, and what data
The letter template filed with California leaves the data types blank, because each recipient’s letter lists their own. TechCrunch, which read the notices filed with several state attorneys general, reports the stolen data includes driver’s licences of 2,567 people in Massachusetts, 3,430 in South Carolina and 1,873 in Rhode Island. The South Carolina figure matches the state notice reported by WLTX, and Uber’s own Rhode Island addendum says about 1,873 residents were affected.
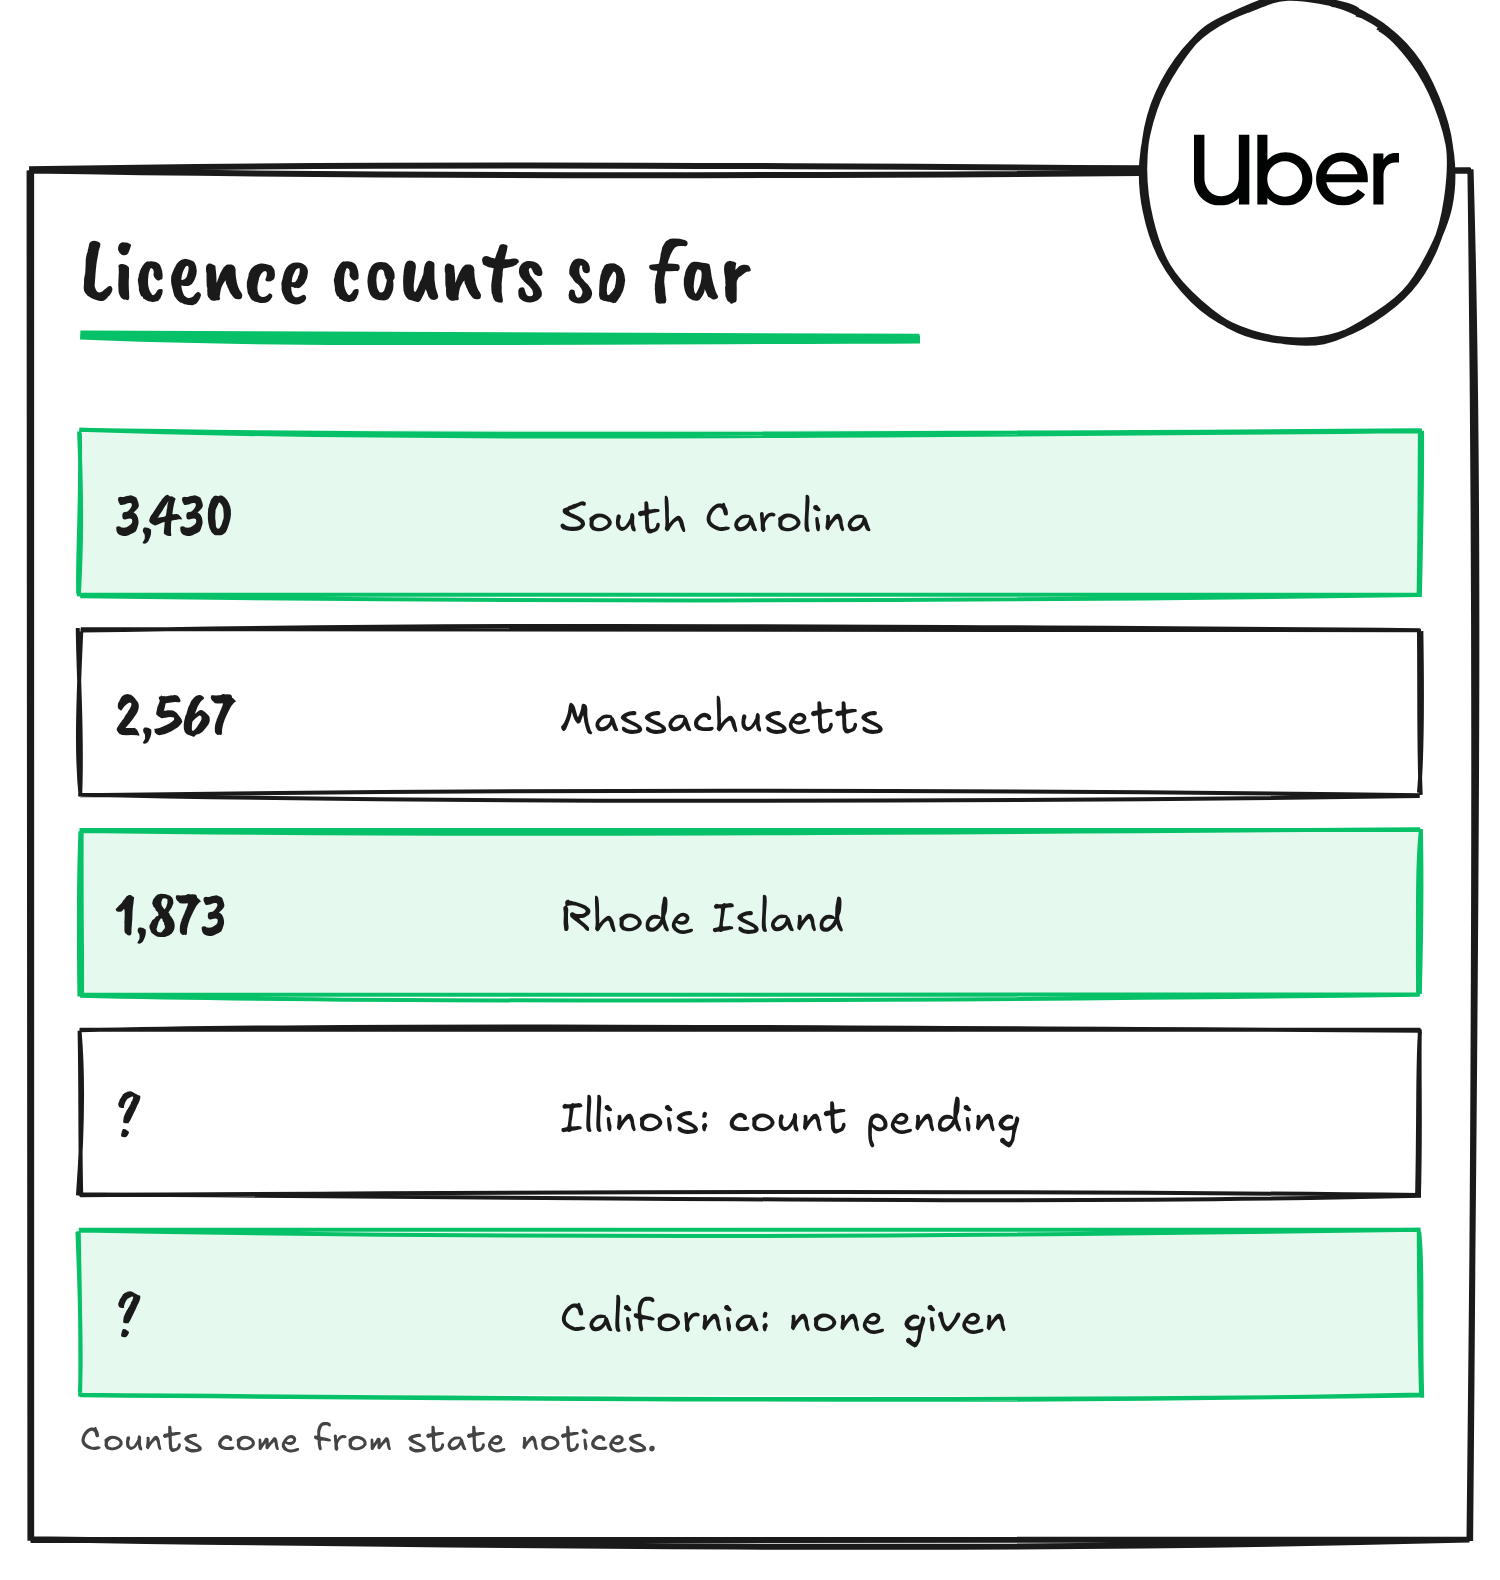
Those three states add up to 7,870 people. Illinois’s filing says some residents had driver’s licence information stolen and lists the count as pending, and Uber notified California drivers without giving a number. Uber hasn’t published a total or said what the data was doing at Fireworks.
What Fireworks has published
Fireworks’ first bulletin says it identified unauthorised use of internal Fireworks credentials on 6 October and notified affected customers at 6pm PDT on 9 October, the day Uber says it was told. That bulletin, last updated on 10 October, says Fireworks hadn’t detected unauthorised access to customer models, datasets, training data or personal information “within the Fireworks security perimeter or control”. The wording covers data inside Fireworks’ own systems, and Uber’s notice describes access through Uber’s account with Fireworks.
Its 9 November update widens that to account and billing information and, for a limited set of accounts, secrets, datasets and incomplete model weights. It also describes a second path: a third-party cloud provider that hosted Fireworks research machines had its own incident on 23 October, and on 24 October the attacker used it to reach Fireworks development machines. The update names resource metadata, billing information, and model weights and datasets as the categories involved. It doesn’t mention Uber, personal information or driver’s licences.
Fireworks says the evidence links the activity to a financially motivated group that sells stolen access to language models. TechCrunch reports that no known criminal group has claimed the Uber data theft. Neither company has said whether Uber’s data was reached through the October credentials or the 24 October path. Notion also said some of its data was in the same incident, which I covered in Fireworks says hack reached billing data and some model weights.
If you get the letter
Uber’s letter gives an activation code for free credit monitoring at mytrueidentity.com, valid for 90 days from the letter’s date. It also recommends checking account statements and credit reports regularly, and says you can ask the three US credit bureaus for a fraud alert or a security freeze. A freeze blocks creditors from seeing your file and can delay new applications.
This is Uber’s second known breach this year, TechCrunch says. The first hit Uber Freight, its trucking unit, and an extortion gang claimed the theft in August.
Discover more from Sulat AI & Tech News
Subscribe to get the latest posts sent to your email.