Anthropic’s Help Center says individual researchers, open-source maintainers and bug bounty hunters can apply to its Cyber Verification Program (CVP) for Defense Access, a tier that includes Claude Mythos 5.2. An individual verifies with a government photo ID and a live selfie, and the page’s checklist for Defense Access lists no CVE, the public ID given to a disclosed software vulnerability.
Anthropic expanded the program on 6 October into three access tiers, and released Mythos 5.2 on 9 November. Anthropic’s Claude Platform docs say Mythos 5.2 is the same model as Claude Fable 5.2, which is generally available, with the cyber blocks relaxed for verified users. It costs US$8 per million input tokens and US$40 per million output tokens.
How an individual applies
- Sign in to Anthropic’s Verification Portal with your Anthropic account and choose “Cyber Verification Program”.
- Choose individual verification. Anthropic’s list for individuals is a government-issued photo ID, as the physical document and not a photocopy, and a phone with a camera for a live selfie.
- Describe your security work, accept the terms and submit.
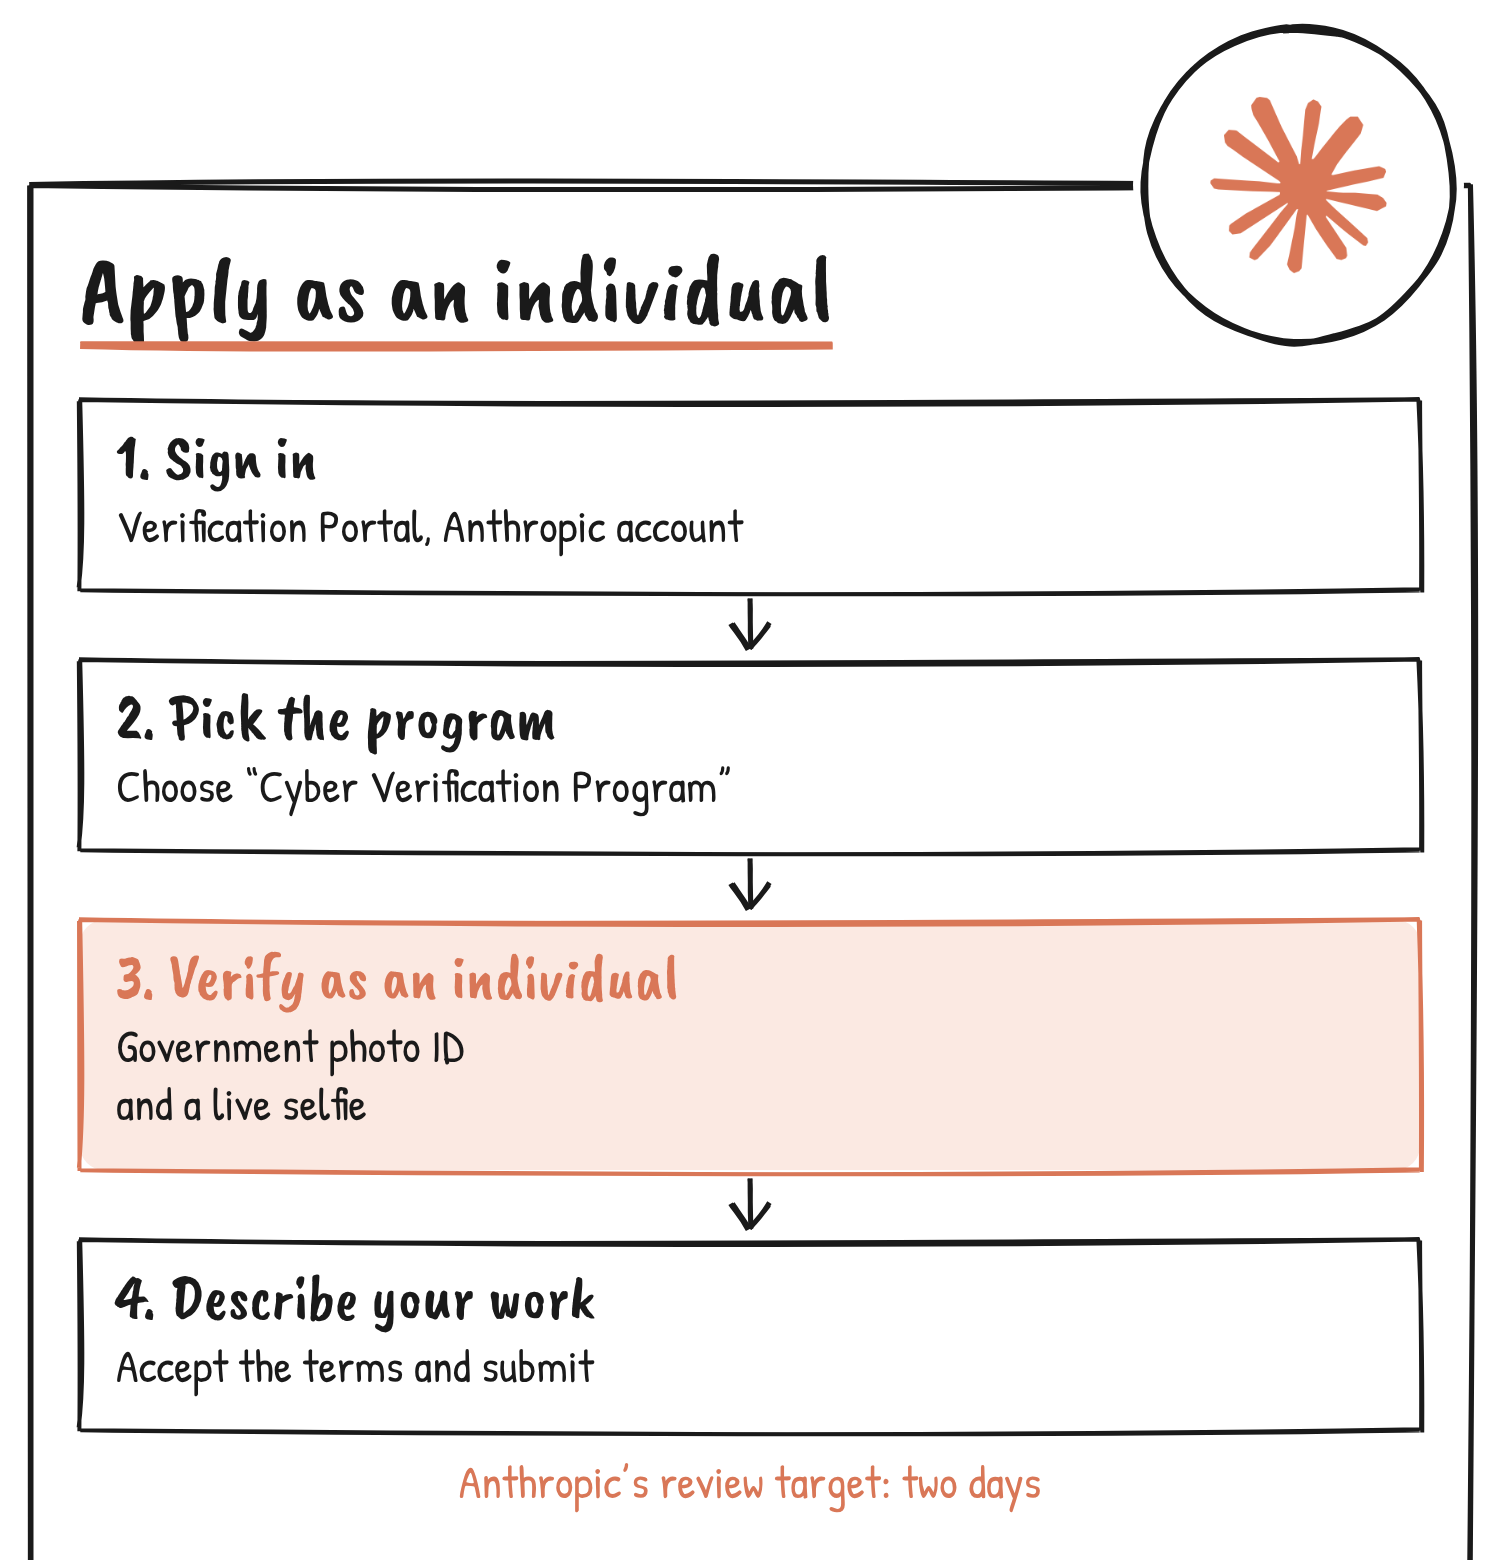
Anthropic’s identity verification page says Persona, its fraud prevention partner, collects and holds the ID and selfie, not Anthropic’s own systems. Anthropic’s review target for Defense Access is two days. If you’re not approved, you can reapply after seven days, and you can’t edit or cancel an application once it’s submitted.
Individuals can apply on a Pro, Max, Ultra, Team, Enterprise or API plan. The program isn’t available on the Free plan.
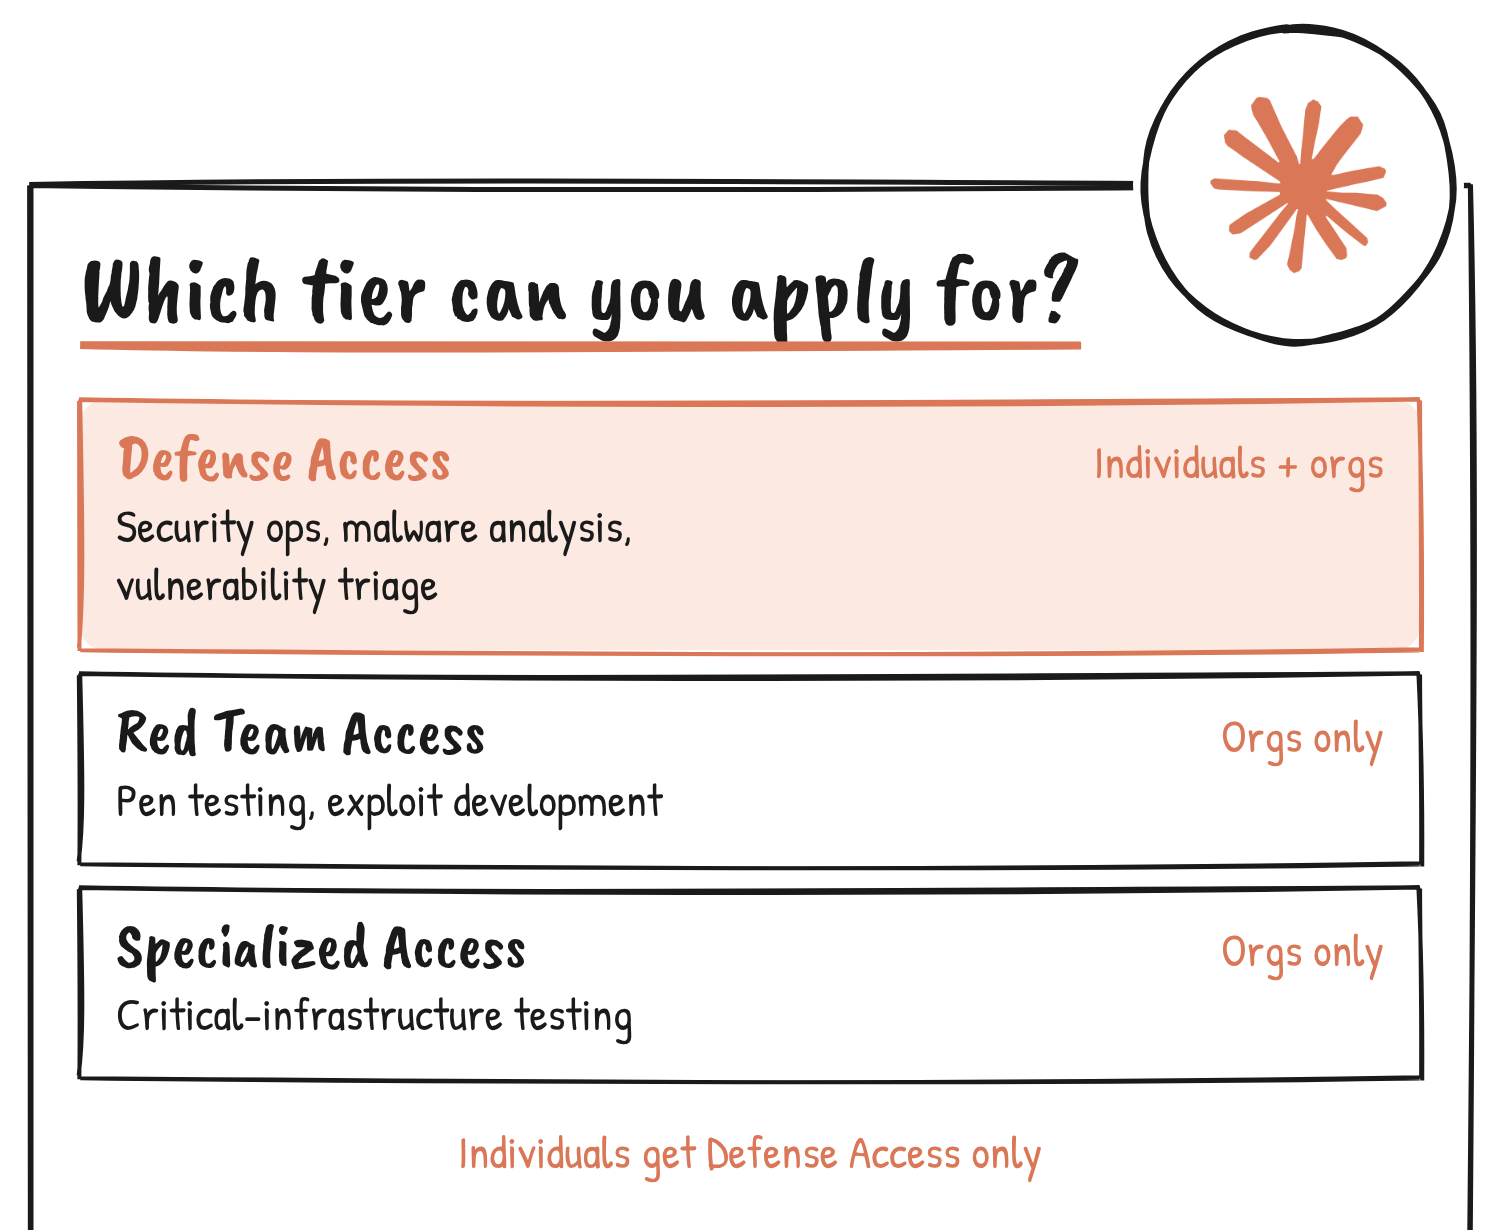
What Defense Access covers
| Tier | Who can apply | What it’s for | Approved users |
|---|---|---|---|
| Defense Access | Organisations and individuals | Security operations, incident response, malware analysis, detection engineering, vulnerability triage and validation | No default limit; individual access covers only you |
| Red Team Access | Organisations only | Authorised penetration testing, red teaming, adversary emulation, offensive tool and exploit development | Up to 75 |
| Specialized Access | Organisations only | Authorised testing of critical infrastructure and research into the highest-severity techniques | Up to 25 |
Defense Access still blocks some work. In Anthropic’s CyScenarioBench test of multi-stage cyber operations on Claude Opus 5.5, Defense Access blocked 46 of 50 trials and Red Team Access blocked none. Every tier prohibits mass destruction of data or devices, denial-of-service attacks, physical-world damage, extortion, election interference and any request with stated malicious intent.
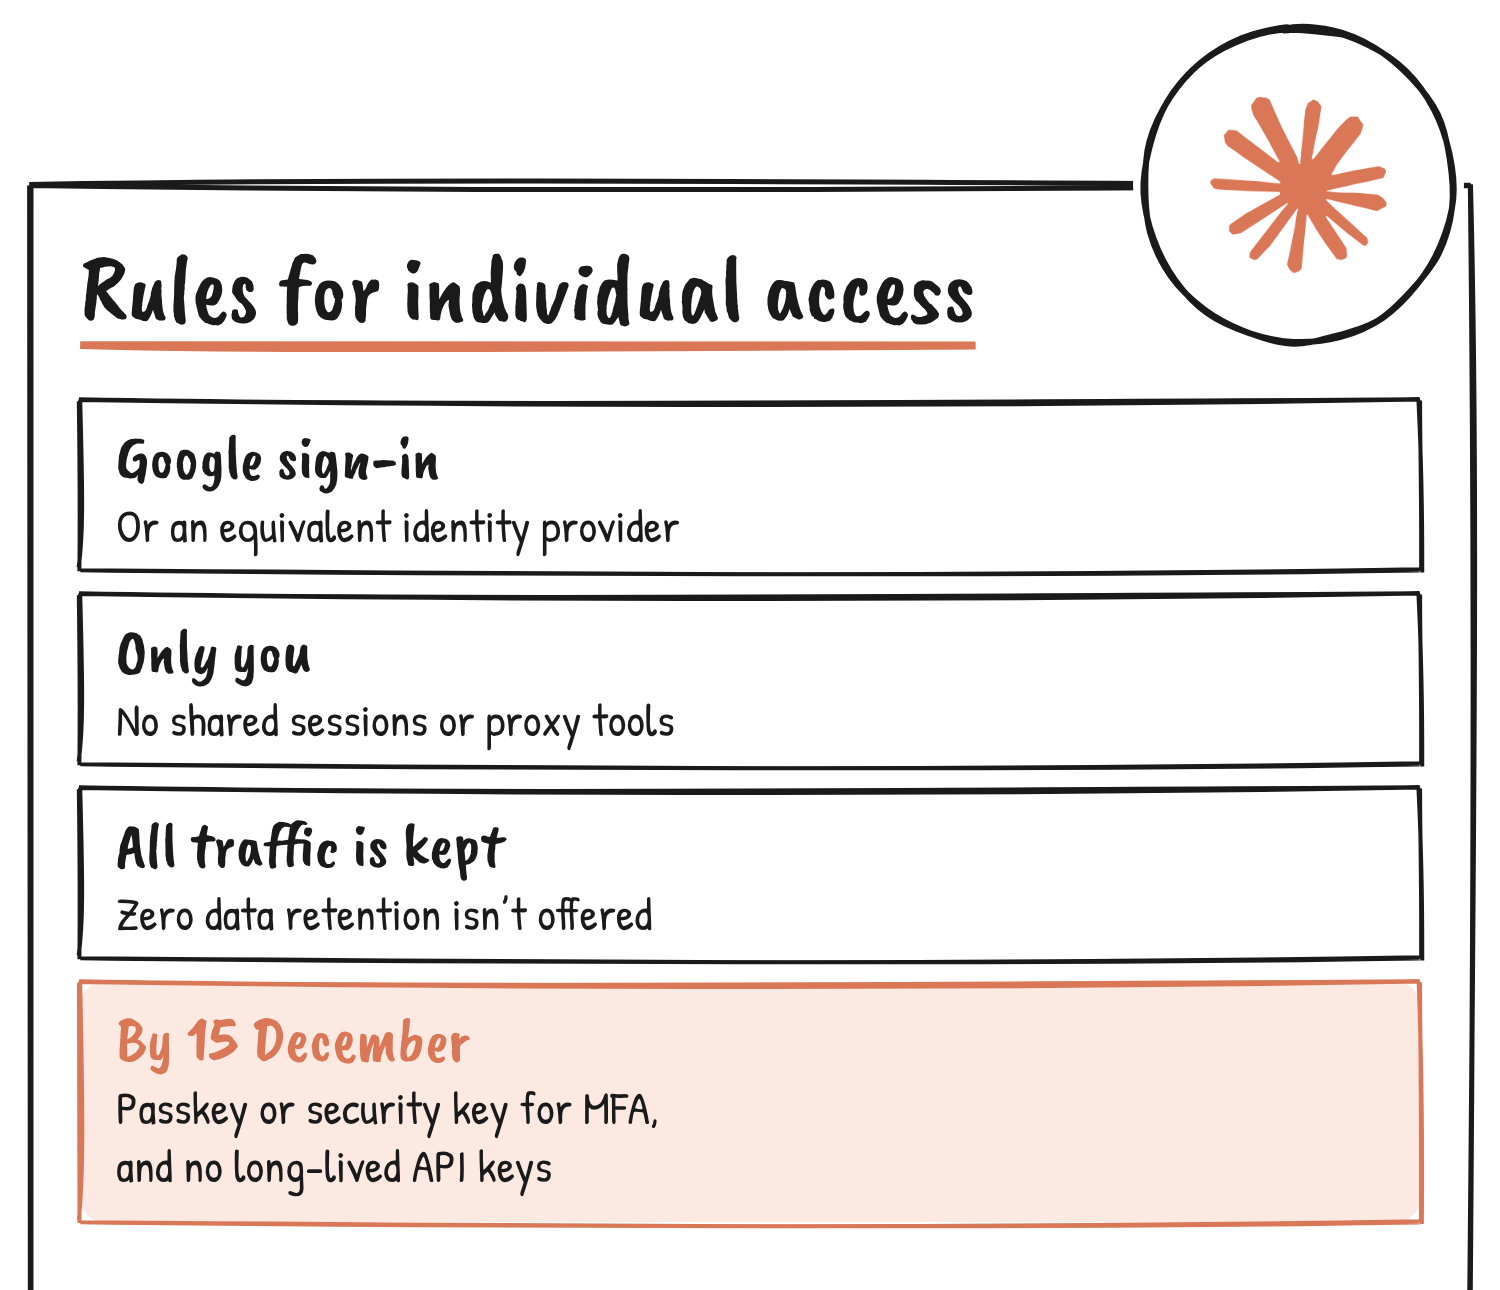
The rules that come with it
Anthropic’s security requirements page has a section for individuals. You must sign in to the Anthropic account that holds the grant through Google or an equivalent identity provider, with multi-factor authentication on from the day access is granted. You’re the only person who can use the access, and shared sign-ins and browser extensions or proxy tools that expose your session to others aren’t permitted.
All traffic under the grant is retained and monitored, and zero data retention isn’t available. Anthropic’s Mythos page says Mythos models need 30-day data retention for safety monitoring by default.
The rules tighten on 15 December 2026. From that date the account needs phishing-resistant multi-factor authentication, meaning a security key, a passkey or a smartcard, and email magic-link sign-in is out. Static or long-lived credentials, including API keys, stop being allowed. Until then, one API key is allowed if it’s kept in a password manager and replaced at least every seven days.
Anthropic says it can review, narrow or withdraw program access at any time if it sees activity that breaks its policies.
What it costs
| How you pay | Mythos usage |
|---|---|
| Pro plan | Available only with usage credits |
| Max and Ultra plans | Mythos and Fable share up to 50% of your weekly usage limit, which also counts toward your regular limits. After that, usage credits if they’re on, or another model |
| Claude API | US$8 per million input tokens and US$40 per million output tokens; fast mode is US$16 and US$80 |
Where Anthropic’s pages differ
Anthropic’s Mythos page says Mythos 5.2 is available to vetted organisations, and the Claude Platform docs say it’s available only to organisations verified through its programs. The Help Center says individuals can apply for Defense Access, which includes the Mythos models.
The October announcement described qualifying individuals as researchers with a track record of reported vulnerabilities. The Help Center’s list for Defense Access asks for identity verification, a description of your security work, the security attestations and the terms. It names no CVE or vulnerability record. It says the portal shows any evidence your tier needs, and that links Anthropic can check independently, such as a bug bounty profile, speed up review. Anthropic hasn’t published approval numbers for individual applications.
Discover more from Sulat AI & Tech News
Subscribe to get the latest posts sent to your email.