PHP News, the publication Eric Barnes and Matt Stauffer launched on 13 October, now has a security advisories page that lists every published advisory for 12 PHP projects in one place. The page says it’s “updated automatically as projects publish them.”
The projects are PHP, Laravel, Symfony, Drupal, Craft CMS, Statamic, TYPO3, Guzzle, Livewire, Composer, Doctrine and Yii. Laravel’s page also covers nine first-party packages and Symfony’s covers four. Six of the projects (Laravel, Symfony, Drupal, Craft CMS, Statamic and TYPO3) have a “stack” filter, and the page can be filtered by severity, from any severity to critical only, with unrated advisories switched on or off.
What’s open on 15 November
A “Needs attention” list at the top of the page shows recent advisories that affect versions still getting security fixes. On 15 November it counted 28 across four projects: Symfony 22, Laravel 3, PHP 2 and Doctrine 1. Drupal, Craft CMS, Statamic, TYPO3, Guzzle, Livewire, Composer and Yii show none open.
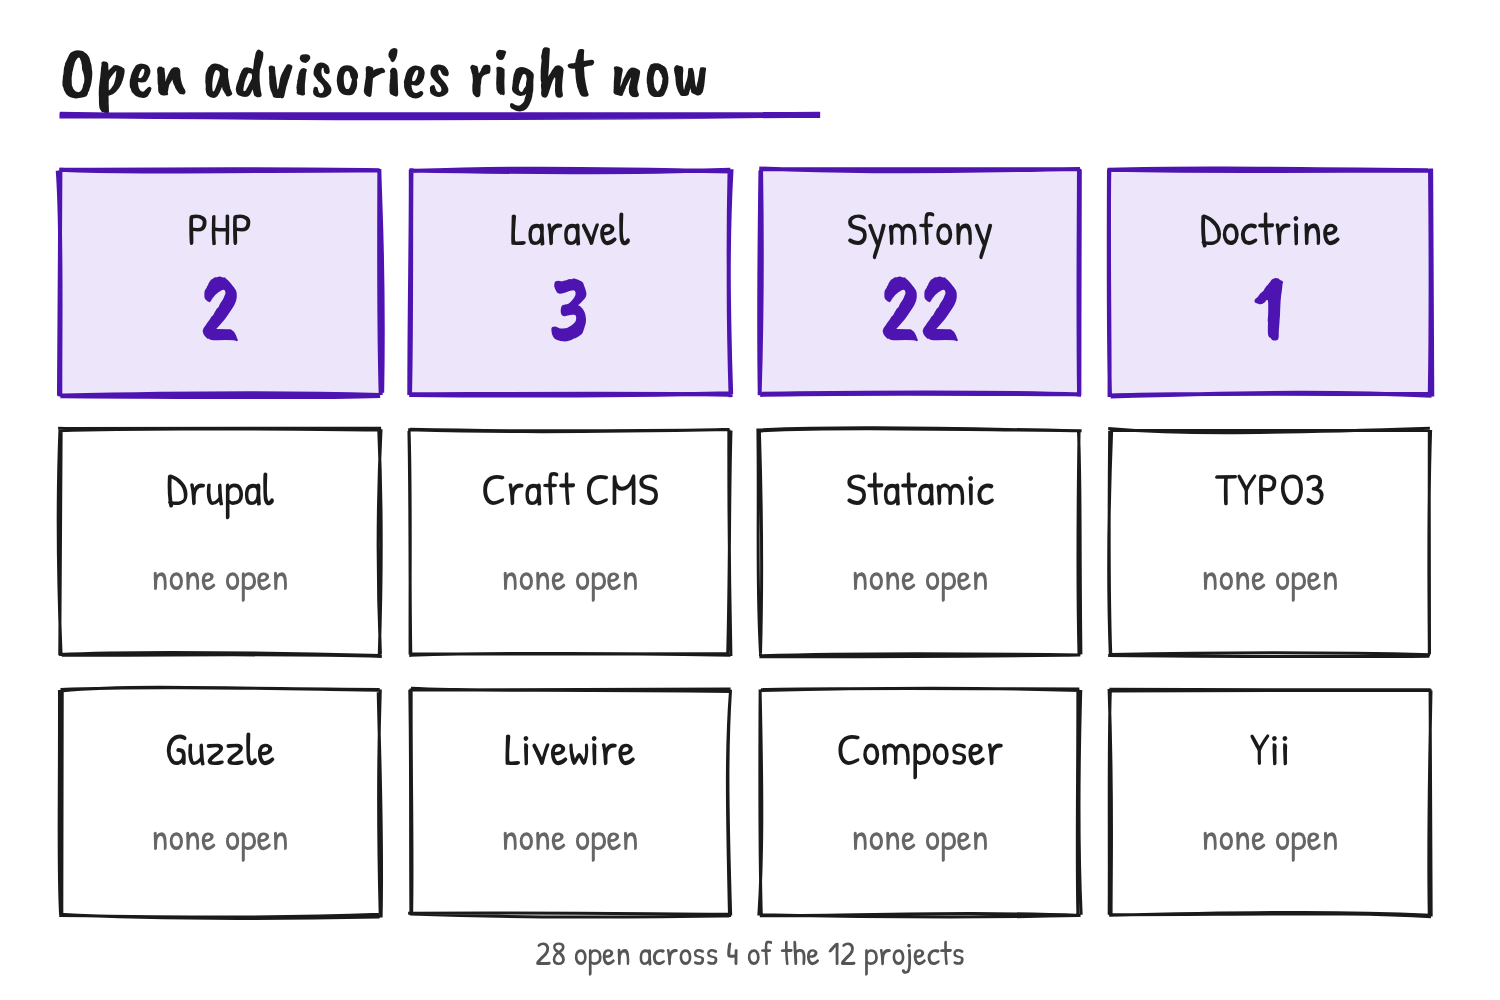
The two PHP entries are the critical remote code execution bugs, CVE-2026-109618 and CVE-2026-109619, which the PHP team fixed on 21 October in 8.5.12, 8.4.27, 8.3.36 and 8.2.35. php.net rates both at CVSS 4.0 9.2.
The Symfony entries date from 4 November, when the project released 5.4.56, 6.4.50, 7.4.23 and 8.1.11 with security fixes across its Routing, Serializer, Config and HtmlSanitizer components, among others. PHP News lists those four versions as the fix. Its three Laravel entries run from a critical TokenGuard bug on 23 October to a low-severity Concurrency bug on 13 November, with 13.40.0 and 12.71.0 as the fixed releases. The one Doctrine entry is a medium-severity MongoDB ODM bug that can store encrypted fields as plain text, fixed in 2.17.3.
What an entry shows
Every entry has a severity label, a date, a title, a one-line impact and an “Update” line with the fixed version for each supported branch. Entries also show a CVE ID where one exists and a “Reviewed” date. The page doesn’t say what “Reviewed” means.
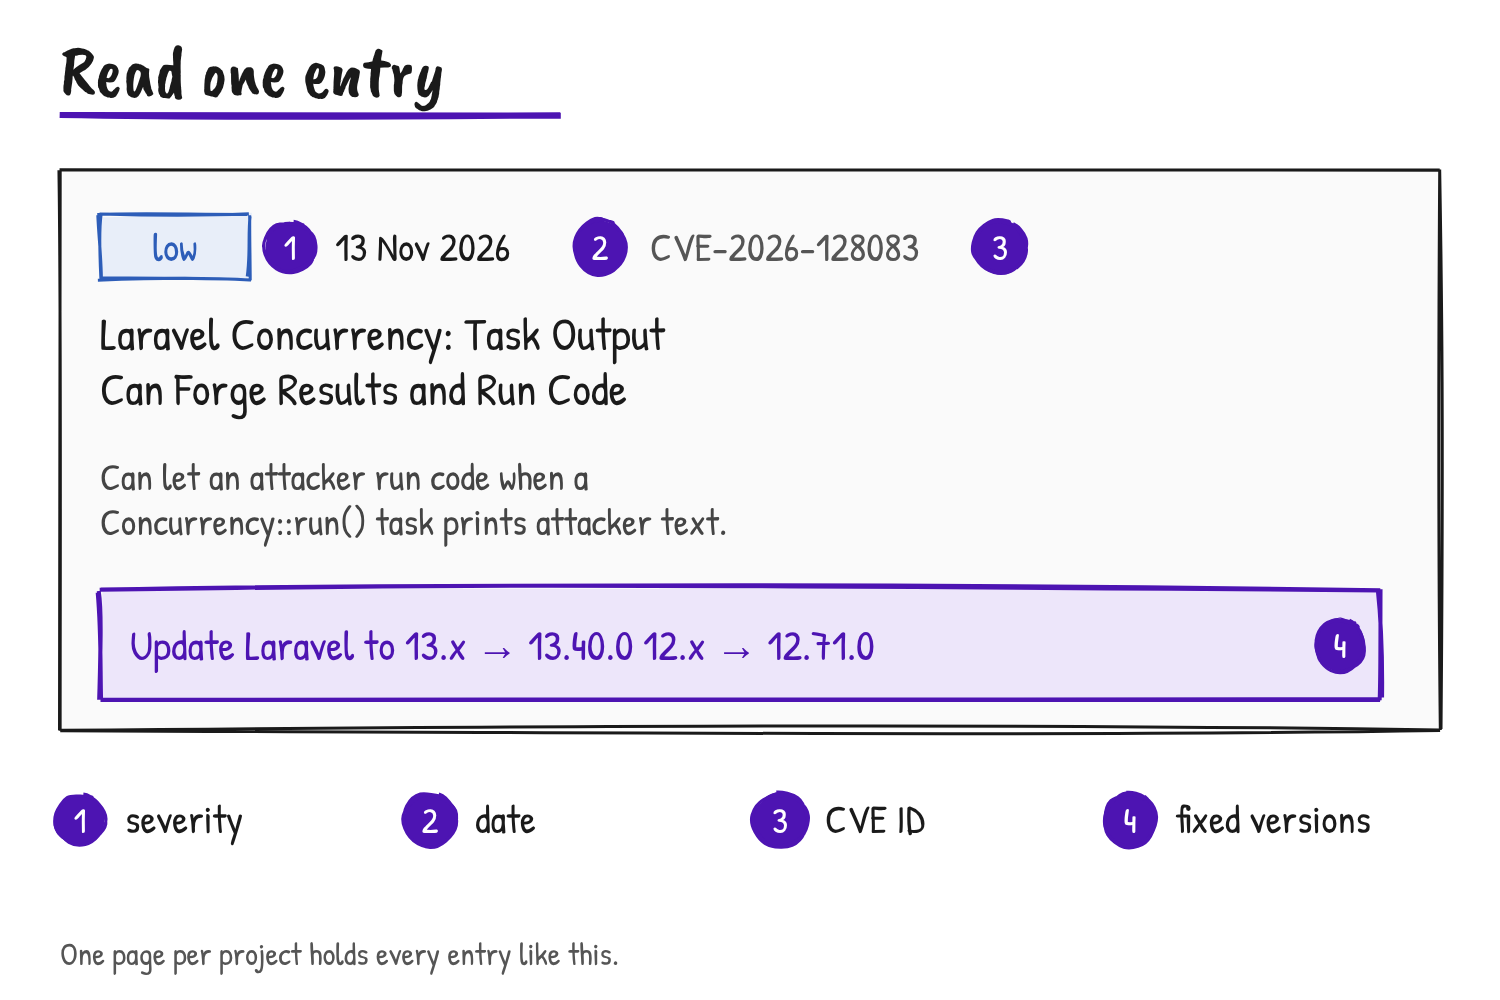
The Laravel Concurrency entry shows how the labels line up with the primary record. PHP News marks CVE-2026-128083 low and says it can let an attacker run code when a Concurrency::run() task prints attacker-controlled text. The CVE record gives it a CVSS 4.0 score of 2.3 and says the behaviour isn’t exposed by default: an application route has to invoke Concurrency::run, and a task has to write attacker-controlled bytes at the start of its output.
Supported branches and the version checker
Each project has its own page with the latest release on every branch that still gets security fixes, and a version checker. On the PHP page, the checker lists every security fix a given PHP version is missing and how long its branch is supported. The PHP page lists 63 advisories in all, and the 12 project pages add up to 421.
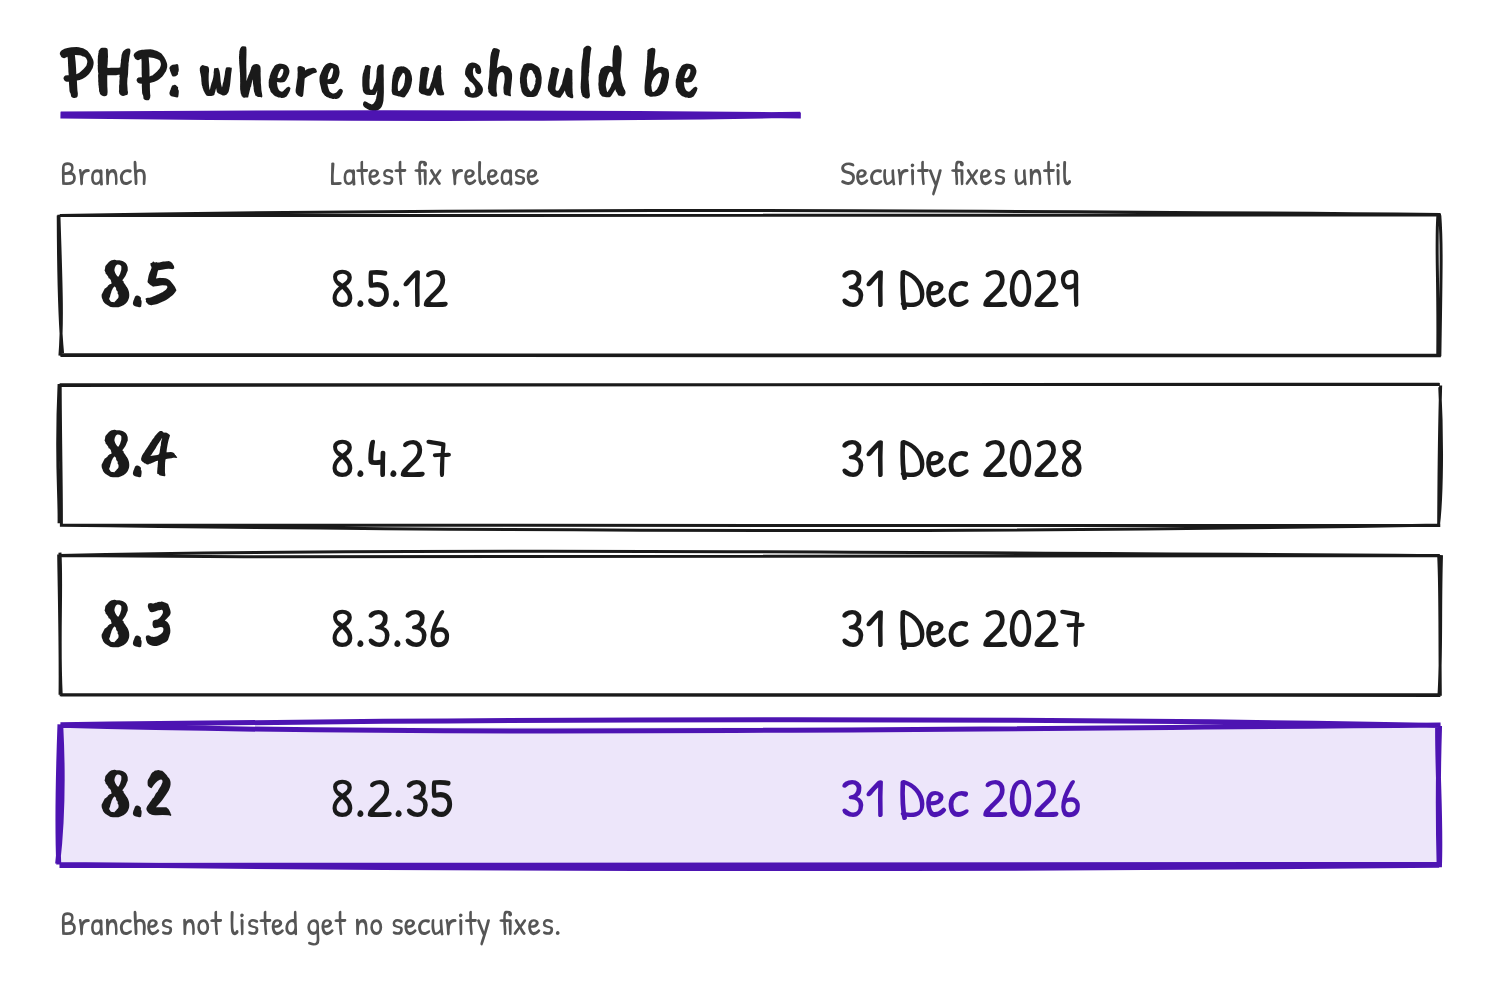
PHP 8.2 is the branch closest to the cut-off. The PHP page gives 31 December 2026 as its last day of security fixes, and php.net’s 21 October release notice says the same. The page gives 31 December 2027 for 8.3, 2028 for 8.4 and 2029 for 8.5.
PHP News says it’s not affiliated with the PHP Group, so php.net stays the source for PHP’s own advisories. The security page carries partner placements for PhpStorm and Tideways, the site’s two launch partners. PHP News also publishes a free weekly email covering releases, RFCs and packages.
Discover more from Sulat AI & Tech News
Subscribe to get the latest posts sent to your email.