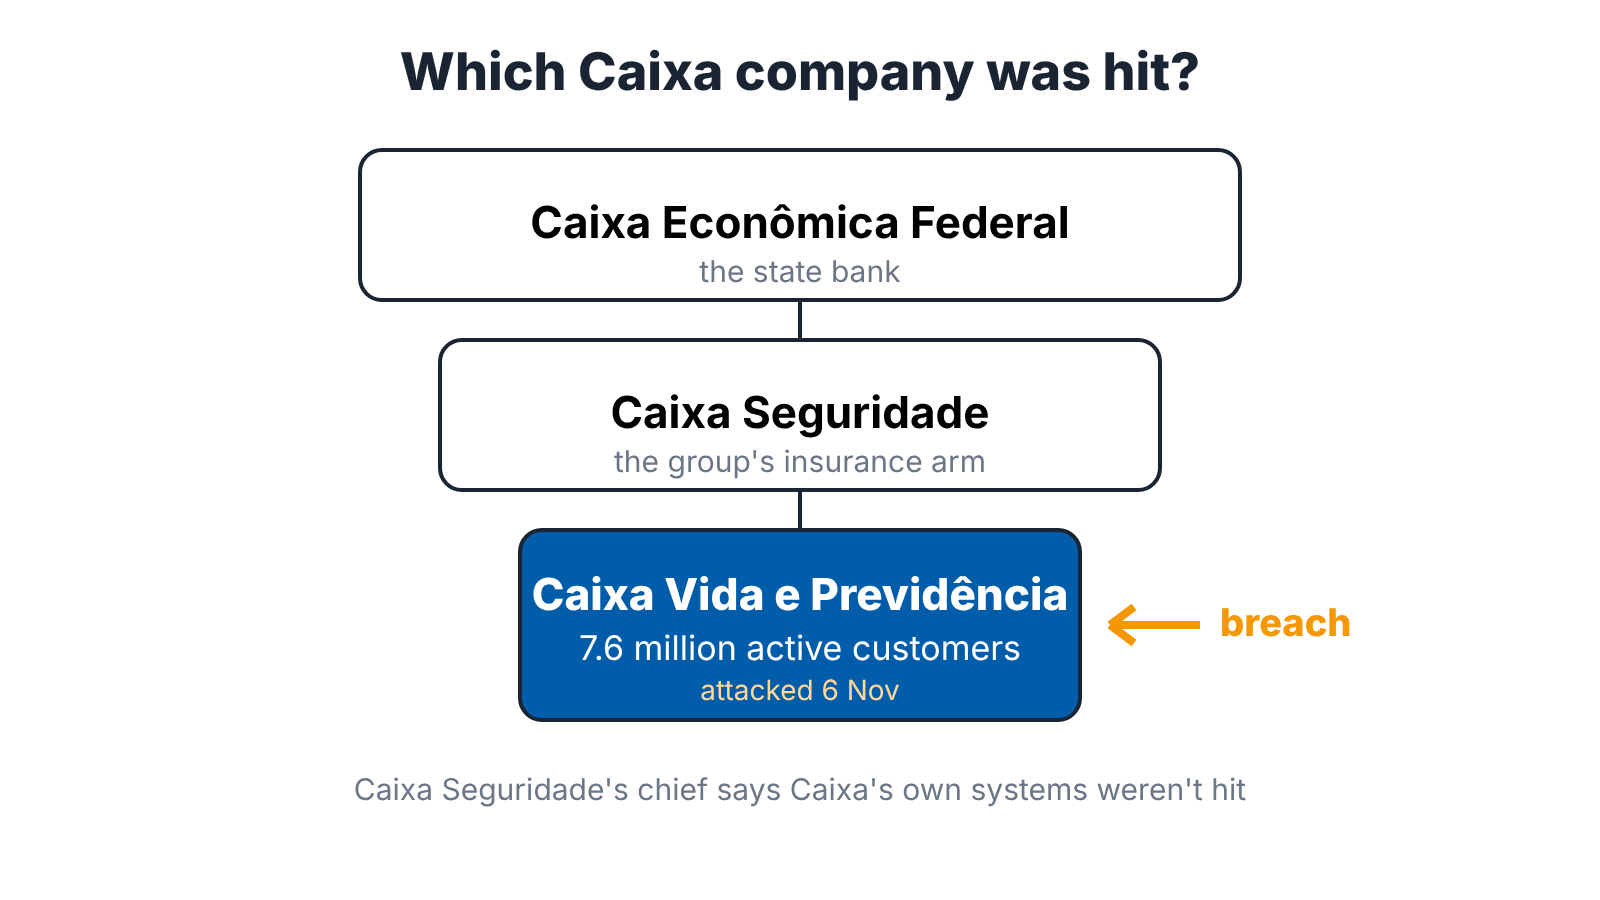
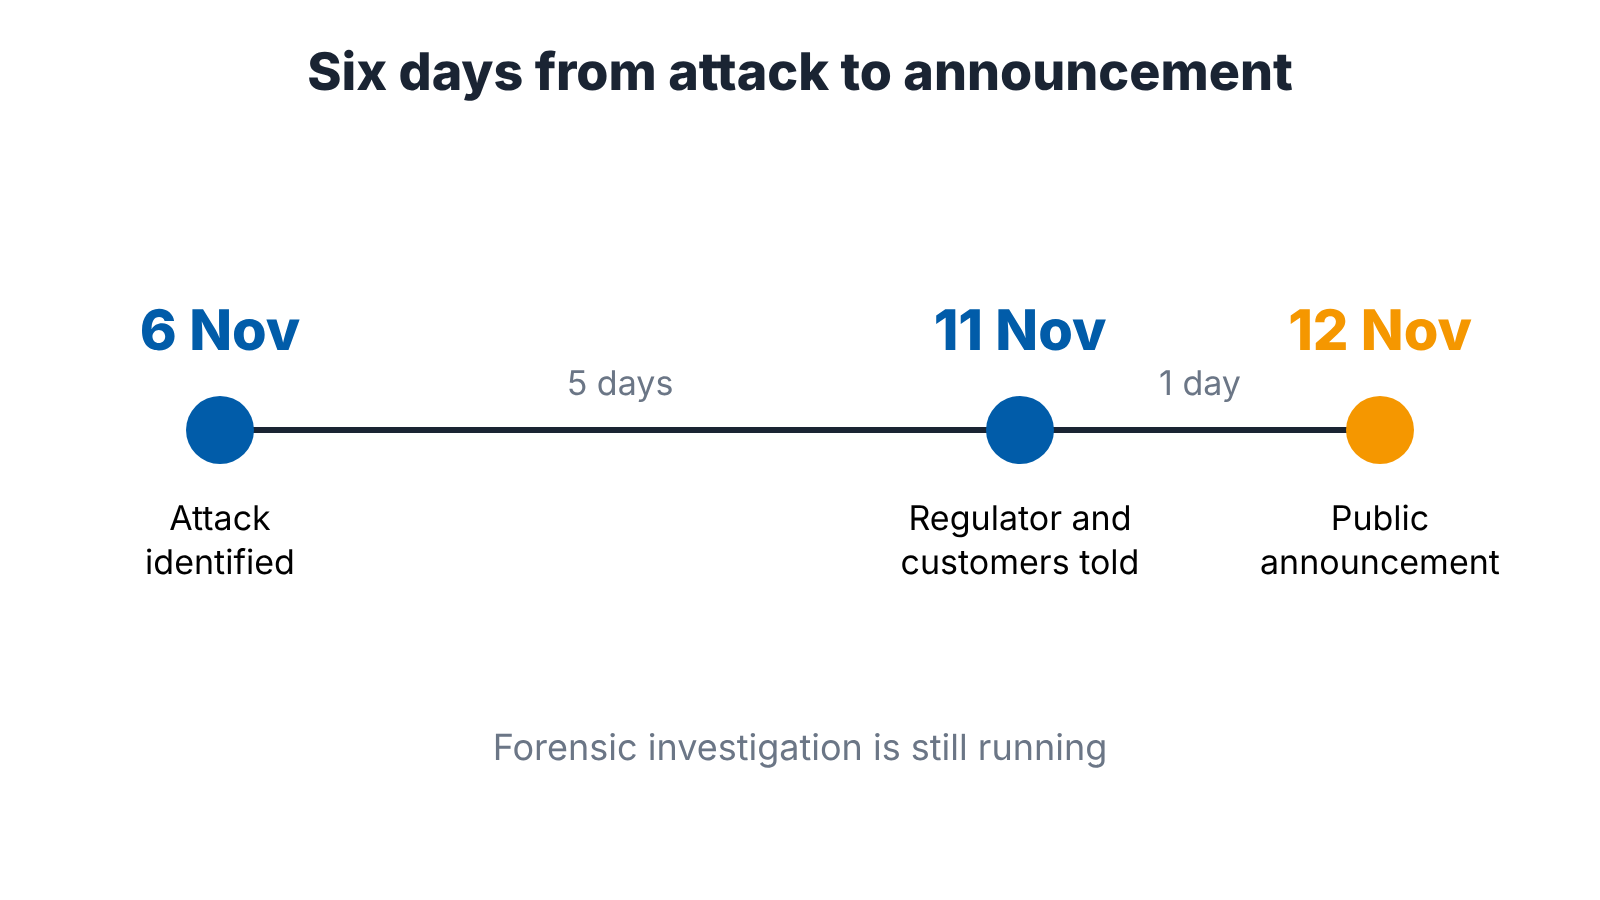
Caixa Vida e Previdência, the life insurance and pension company in the state-owned Caixa Econômica Federal group, says attackers copied personal data on all 7.6 million of its active customers. Its parent, Caixa Seguridade, told the market on Thursday 12 November that the attack happened on 6 November. Records on former customers were copied too. Caixa Seguridade’s chief executive, Gustavo Portela, said Caixa’s own systems weren’t affected.
What was copied
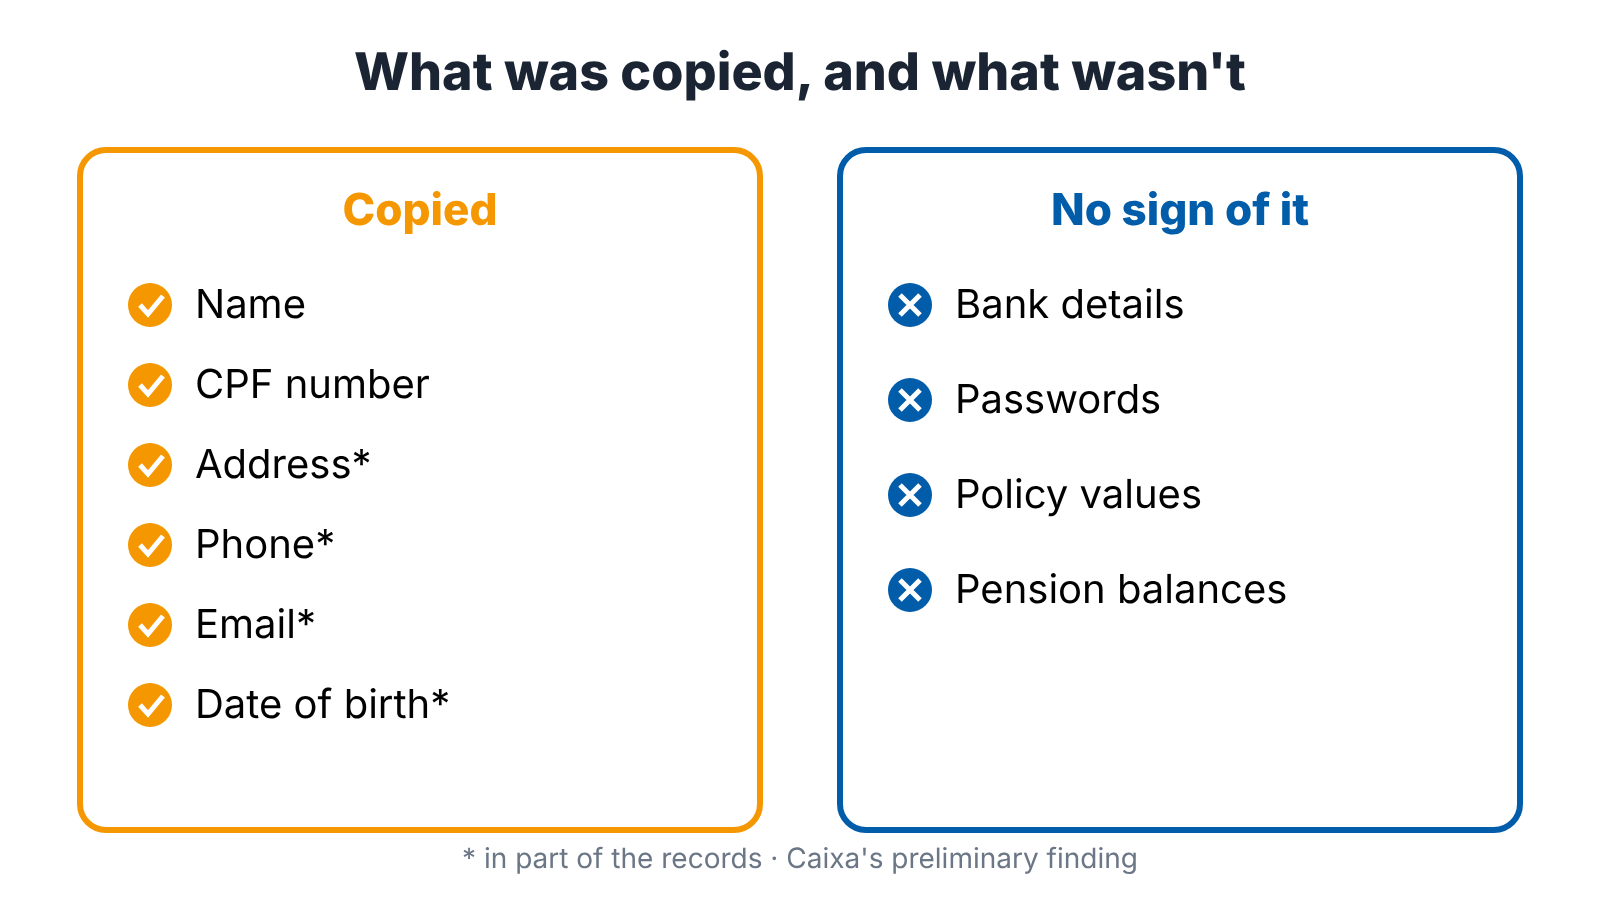
The copied records hold names and CPF numbers, Brazil’s taxpayer IDs. In part of the records, the attackers also got addresses, phone numbers, email addresses and dates of birth. The company’s preliminary finding is that nothing shows financial or login data was compromised, which covers policy values, pension balances, bank details and passwords. Portela described the exposed data as customer data rather than sensitive data, mostly names and CPFs.
What the company has done
Caixa Vida e Previdência says it found and blocked the methods used in the attack, added protections and hired an outside forensic firm to establish where the attack came from and how far it reached. It’s also watching the internet for signs that the data is circulating. As of its statement, it had found no evidence that the data was published or misused, according to Estadão’s TecMundo.
The company told Brazil’s data protection authority, the ANPD, on 11 November, along with other authorities and the people affected, as the LGPD data protection law requires. Customers whose phone numbers or email addresses were exposed, and members of vulnerable groups, are getting guidance on avoiding fraud, and the company has opened an email channel for questions. In a statement to me on 19 November, the ANPD said it received the company’s incident notification on Wednesday 11 November and is reviewing the measures taken, especially on transparency and on limiting harm to the people affected. Its General Coordination of Security Incidents has started analysing the preliminary documentation, the company is still within its deadline to supply more information, and the ANPD will ask it for further clarification if it needs to. Caixa Vida e Previdência hasn’t said who carried out the attack or how they got in.
What Caixa’s president said
Caixa president Carlos Vieira addressed the attack on 13 November while presenting the bank’s third-quarter results. He called hacker attacks a global war and the new normal, and said the bank had cut successful attacks that cause financial losses by 50% over a year. He said the group has set up a cybersecurity directorate under its risk and technology vice-presidencies.
Pix problems the same day
Caixa’s Pix payments were also unstable on 12 November, the day the breach was announced. By 1pm in Brazil, Downdetector showed more than 1,000 complaints, mostly about the app. G1 reported there’s no indication the outage is tied to the attack. Caixa hadn’t replied to G1 when it published. I asked Caixa’s press office, Caixa Seguridade’s investor relations, the ANPD, the Banco Central and the Finance Ministry for comment on 19 November. The Finance Ministry’s press office replied the same day and referred questions about the incident to Caixa’s press relations.
Hero illustration features the Caixa logo, which remains the trademark of its owner.
Discover more from Sulat AI & Tech News
Subscribe to get the latest posts sent to your email.